Attack Surface Monitoring
One Attack Surface. Ten Connected Capabilities.
From continuous discovery and evidence-based attribution to dark web intelligence and third-party risk, every finding enters one consistent, actionable view of exposure.
ClearSkies ASM is a continuously operating exposure program rather than a periodic vulnerability scan. Ten capability areas run from first discovery to a closed-out remediation decision.
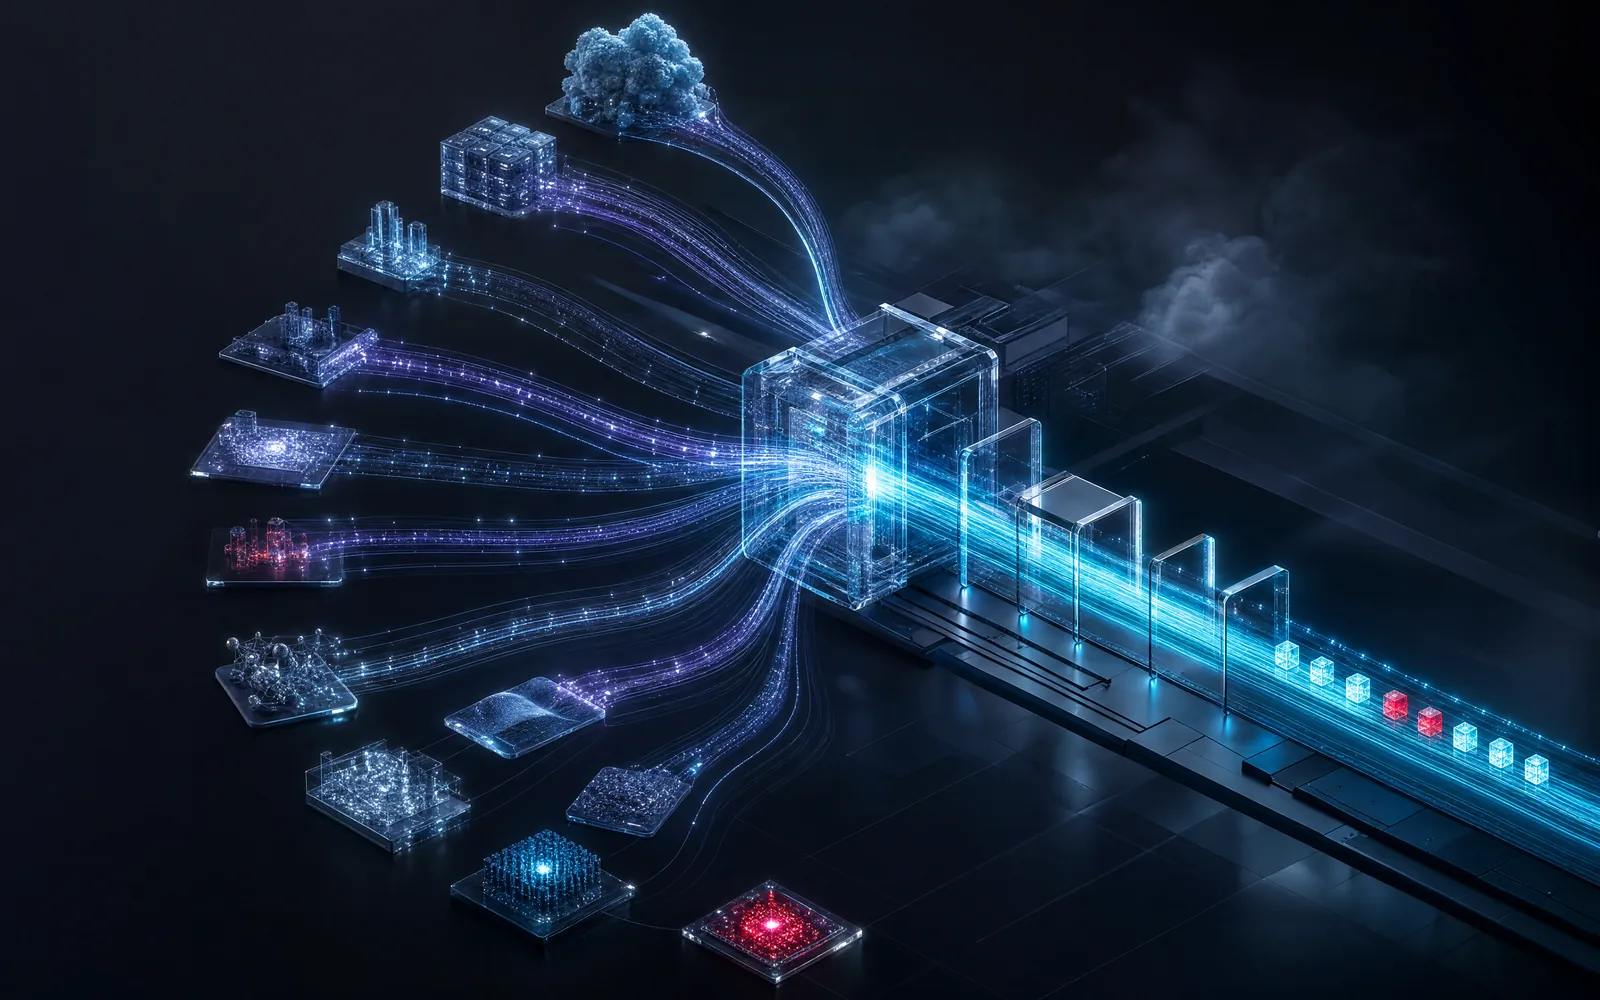
The ten capability areas
Every finding any of them raises carries the same five severity bands, critical, high, medium, low and informational, and the same four confidence bands, so the queue reads the same way whichever capability produced the entry.
Discover Beyond the Known Inventory
The full external surface rather than the recorded one, corroborated across independent sources before anything enters inventory.
Prove Ownership With Multiple Signals
An end to chasing false positives on shared addresses and third-party assets, with a defensible evidence trail behind every attribution.
Prioritize the Risk That Matters Most
A work queue ordered by what attackers are actually exploiting, against assets that actually matter to the business.
Track What Changes, Not Just What Exists
Alerting on what is new rather than on the same finding every morning, with a reconstructable history behind every asset.
Measure Remediation Against Defined SLAs
Remediation measured against agreed time-to-fix targets, with attainment visible to executives and clients.
Operate Across Every Customer From One Platform
A productized service across many customers from one deployment, rather than a custom build per client.
Move Every Finding to a Defined Outcome
Every finding carried to a defined end state, with the reasoning captured and the work done in the tools teams already use.
See Threats Beyond Your Visible Surface
Advance warning of what attackers already hold, evidenced to a standard that survives a board conversation.
Detect Hostile Infrastructure as It Emerges
Reputation and registration signals as first-class inputs, so a hostile address or a fresh look-alike is caught as it appears.
Bring Third-Party Risk Into the Same Register
Vendor exposure and shipped-component vulnerabilities landing in the same risk register as first-party findings.
A Closer Look at Discovery and Prioritization
The two below carry the argument.
Discover What Internal Inventories Cannot See
Nothing can be defended that has not been found, and corroborating across independent sources is what keeps the inventory trustworthy rather than merely large. It is also what lets shadow IT, forgotten development environments, dormant acquisition infrastructure and misconfigured cloud storage surface at all. None of them appear in a configuration management database, precisely because nobody recorded them.
Prioritize by Exploitability and Business Impact
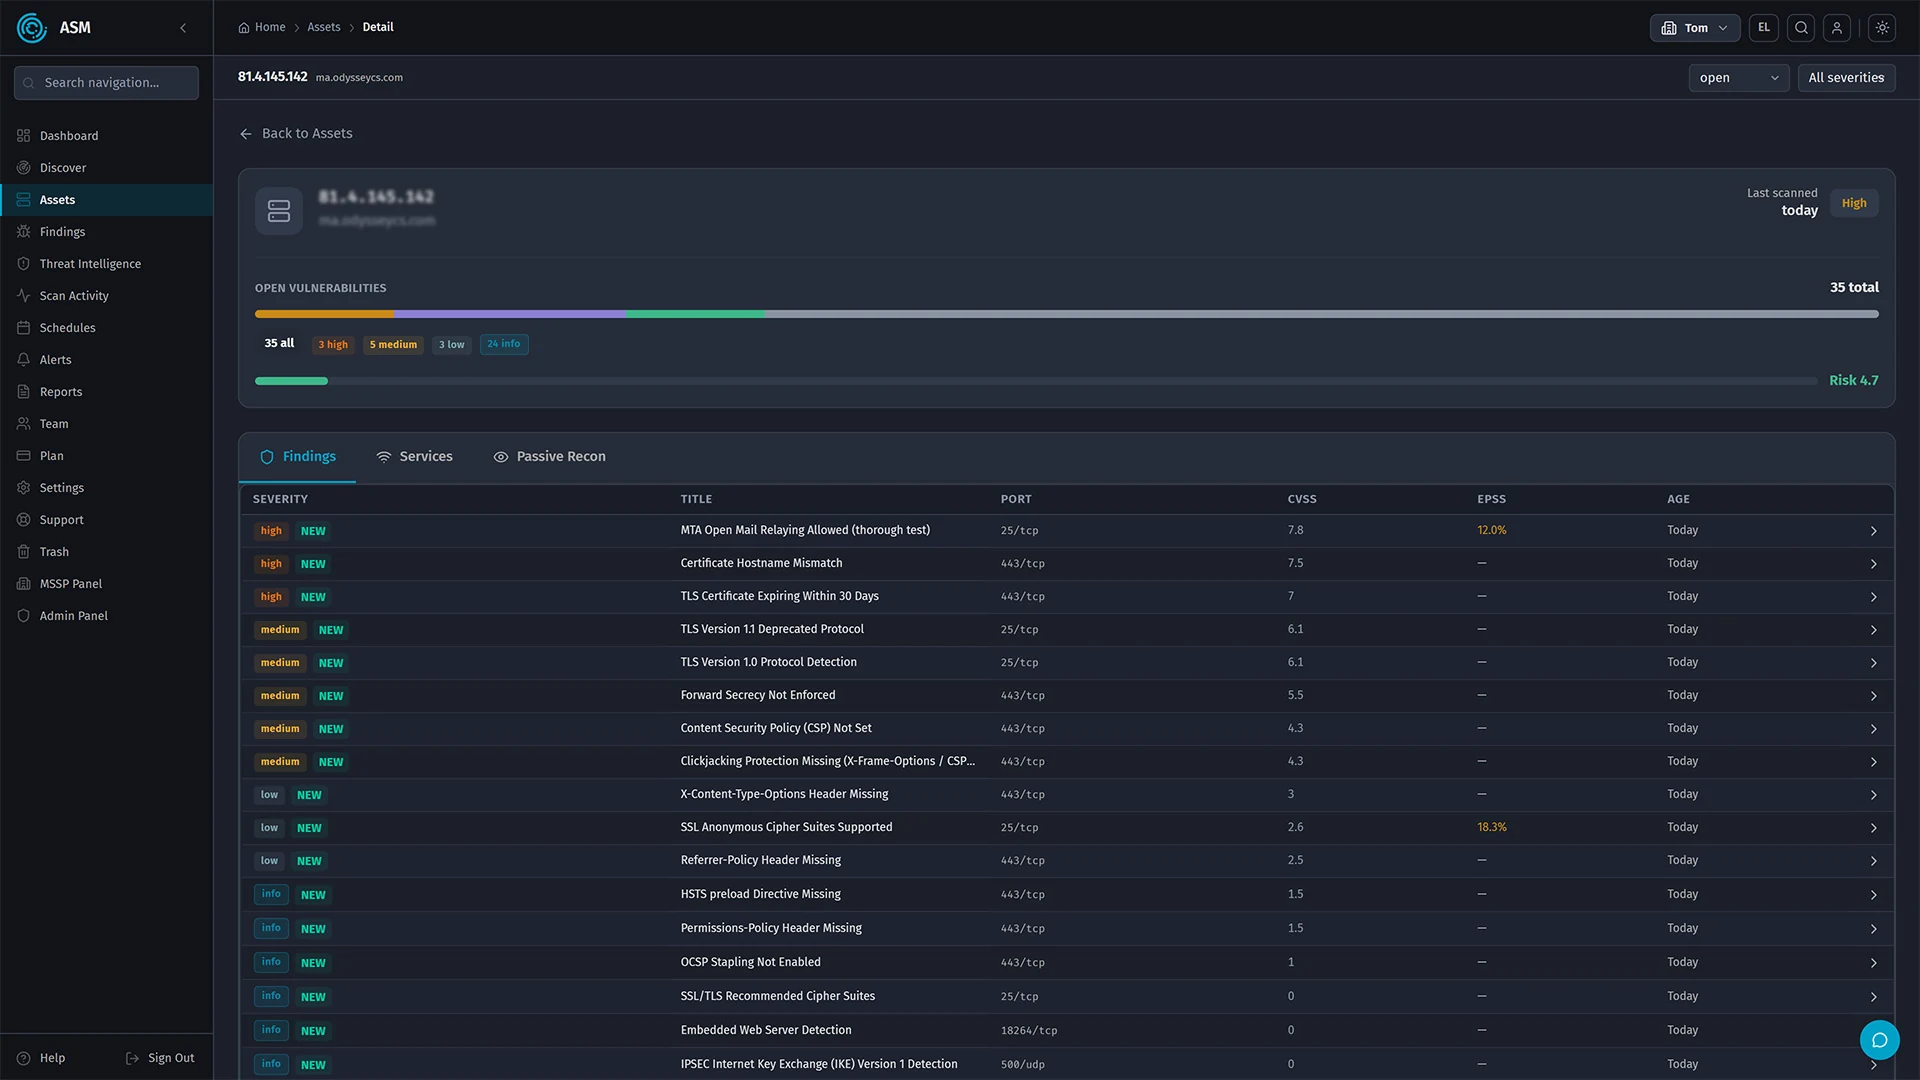
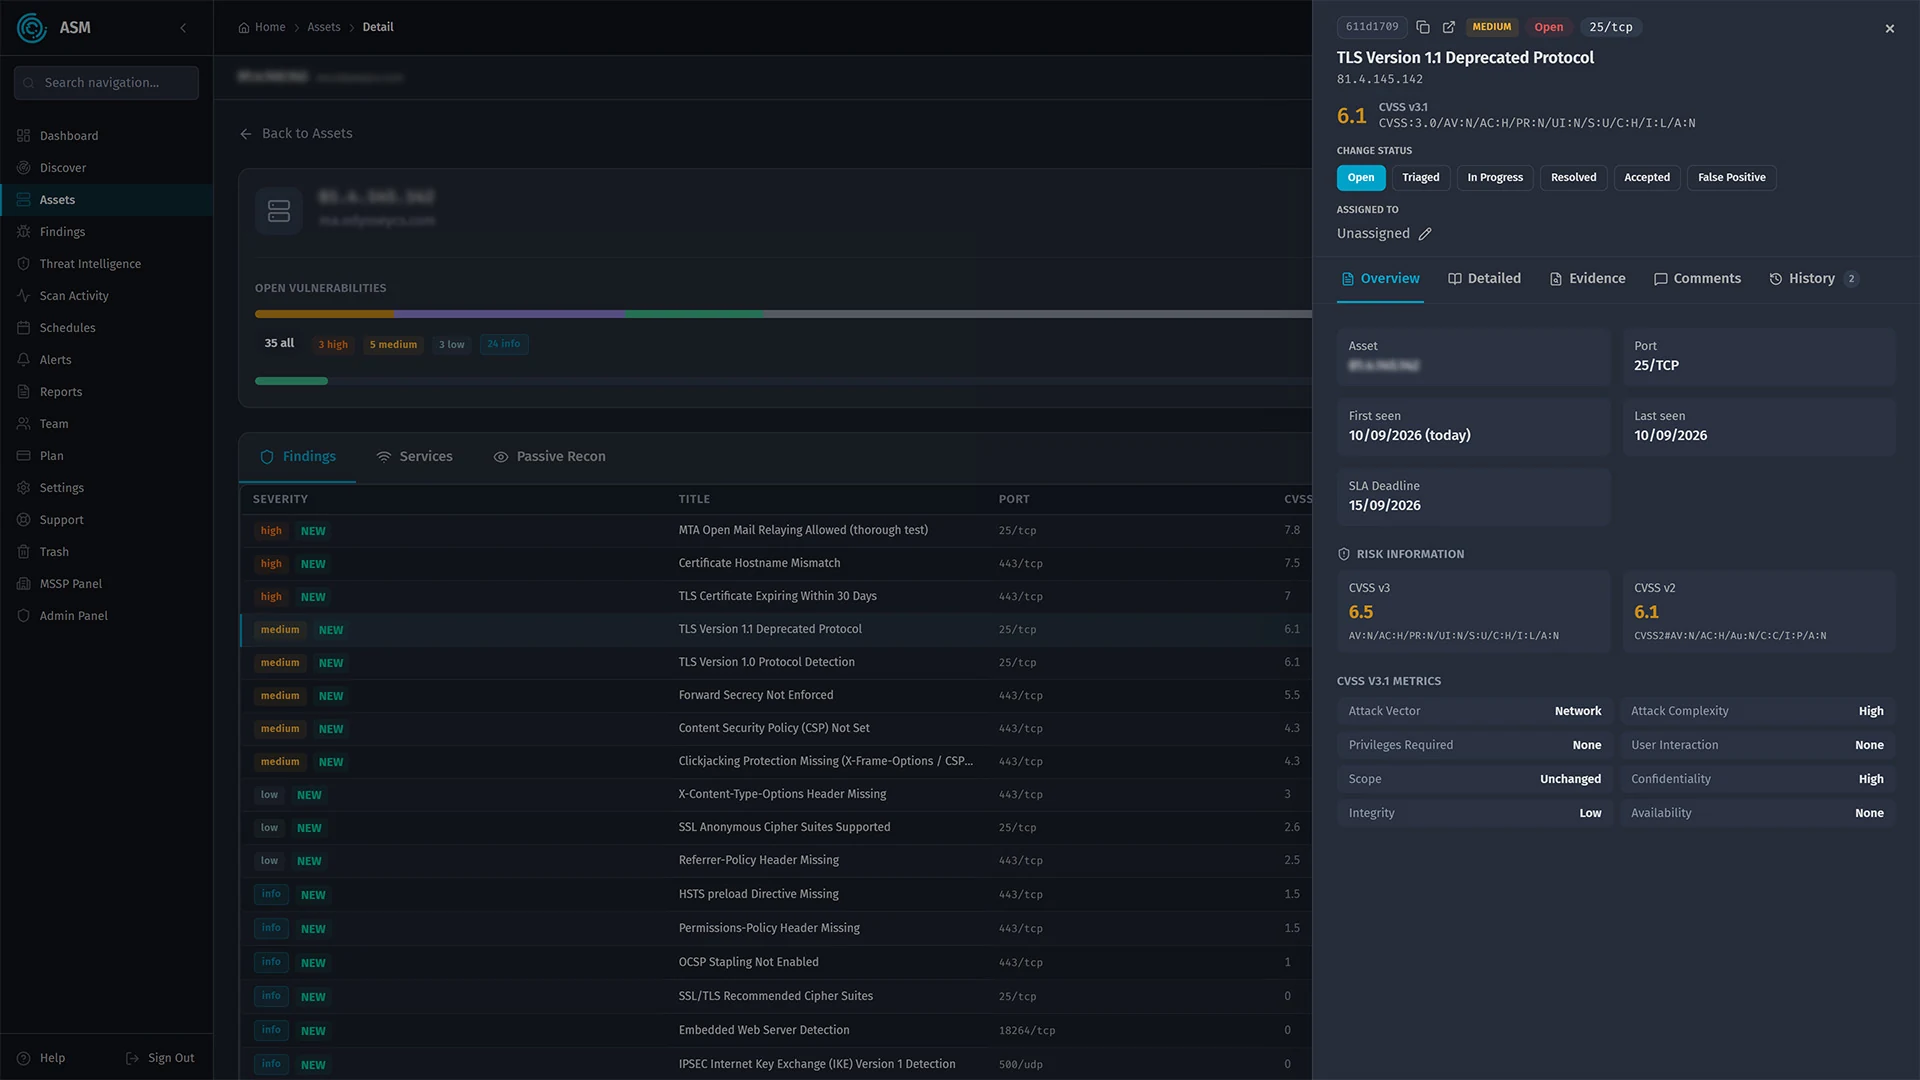
A high CVSS score says how bad an issue would be, not how likely anyone is to use it, so ClearSkies ASM reads CVSS severity, the EPSS exploitation probability and CISA KEV status together, then weighs them against the business context of the asset, so a critical finding on a test box does not outrank a real exposure on a production system.
See What Attackers
Already Know About You
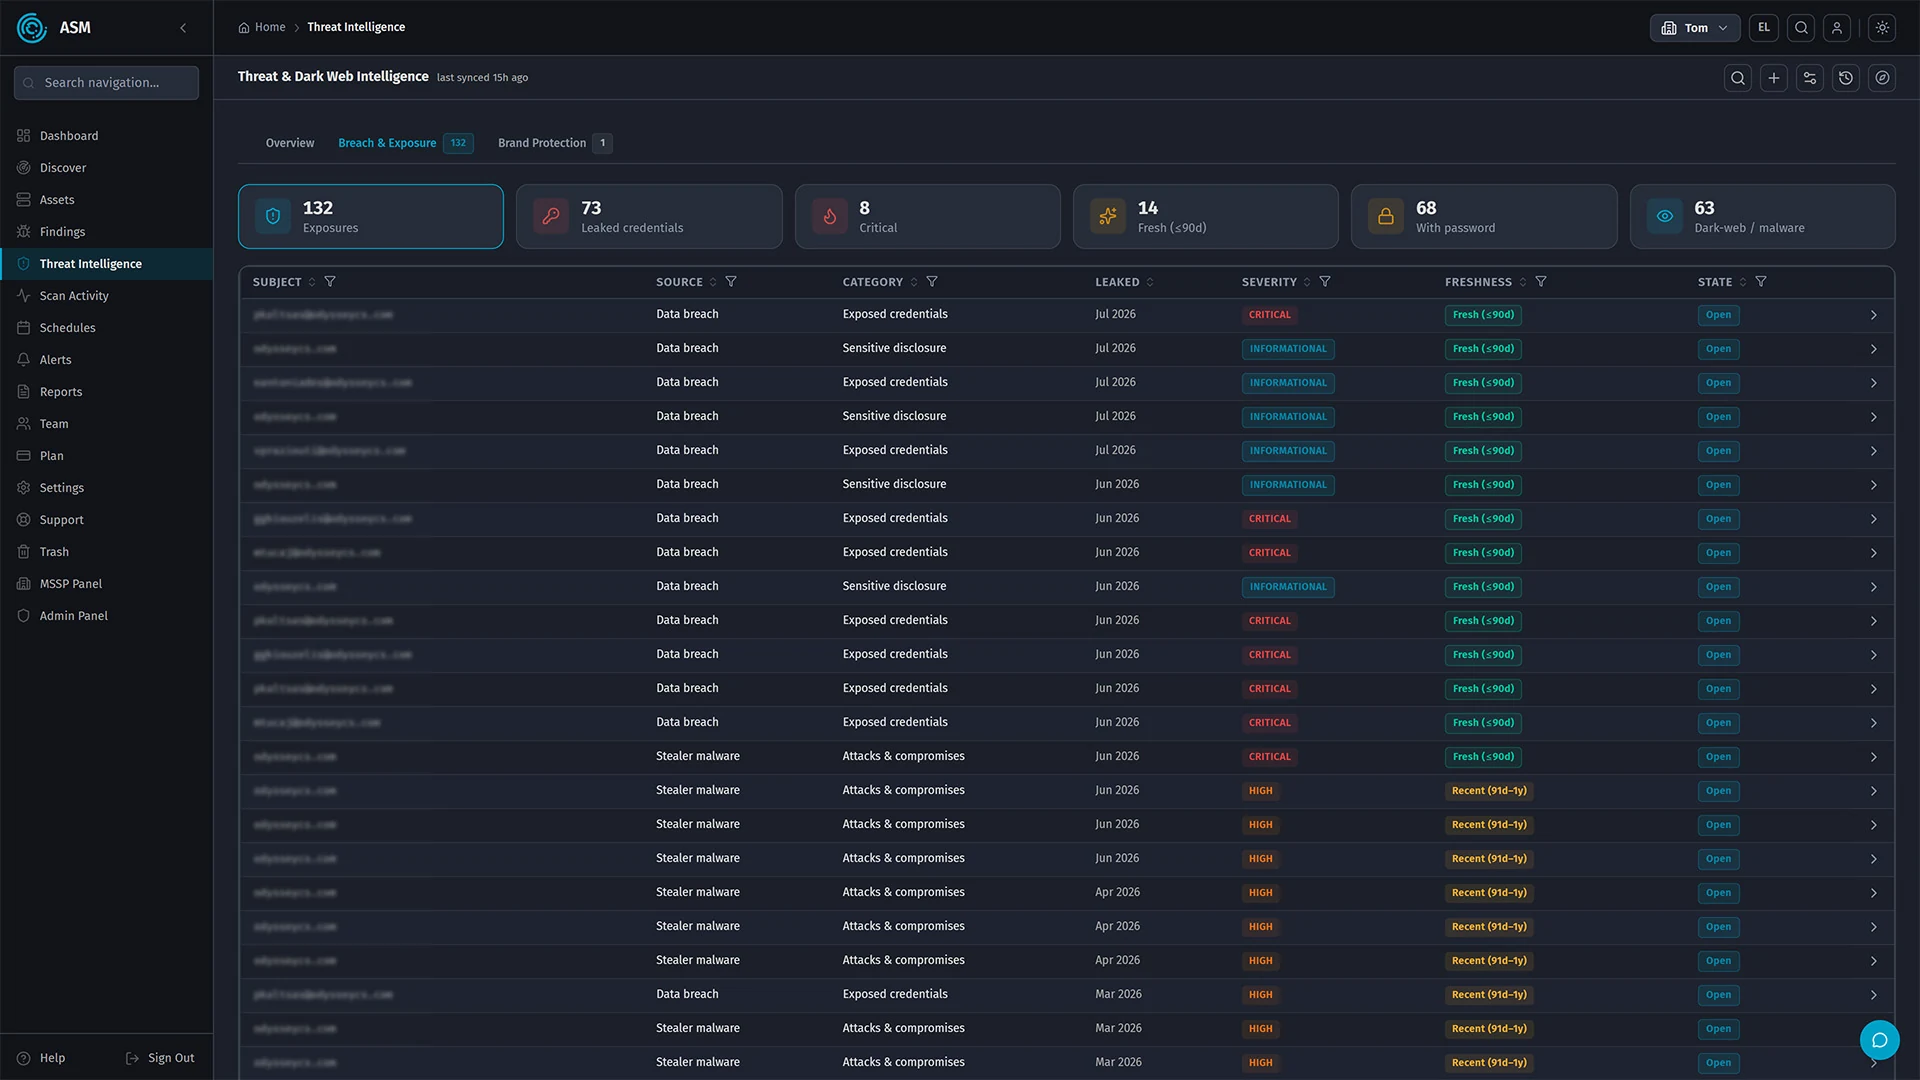
The exposures that hurt most are often already traded before anyone inside the organization sees them: a set of working credentials, a copy of corporate data on a leak site, a look-alike domain waiting to be pointed at customers. None of these sit on the organization’s own infrastructure, so no amount of external scanning will find them.
ClearSkies ASM monitors underground forums, marketplaces, ransomware leak sites, credential shops and threat-actor communications continuously, against the same authorized root domains that scope everything else. It is included per root domain rather than sold as a second subscription, and four things come out of it.

Two things make this more than a feed. First, the evidence bar: a leak finding surfaces only once two independent signals support it, because a leak claim reaches executives and customers before anyone has a chance to verify it, and a wrong one costs more than a missed one. Second, the join to the real surface. A credential is checked against the domains the organization actually operates, and a look-alike domain against the brands it actually owns, so a generic claim naming a large company does not fire an alarm in a tenant that has nothing to do with it.
Findings carry the same five severity bands and four confidence bands as everything else and land in the same register, so a dark web finding is worked exactly as an exposed service is, to the same time-to-fix target. A service provider gains a further vantage point, because the same typo-squat pattern across several unrelated tenants in one week is a campaign no single customer can see.
Threat intelligence answers what is happening in general. Dark web monitoring answers what the underground is saying about this organization specifically.
One Finding. Security and Compliance Context Included.
A SecOps analyst needs to know what an attacker was trying to achieve, which the ATT&CK mapping states. An auditor or a board committee needs to know which control obligation it speaks to, which the framework mapping states. ClearSkies ASM produces both from one tagged finding.
| Capability | ATT&CK tactic |
|---|---|
| Compromised credentials | Credential Access, Initial Access |
| Brand protection | Resource Development |
| Breach and exposure | Exfiltration, Impact |
| Planned-attack early warning | Resource Development, Initial Access |
| Address and domain intelligence | Reconnaissance, Resource Development |
| Domain age and reputation | Resource Development, Initial Access |
ATT&CK coverage is only as honest as the inventory it is measured against, so it is reported against the confirmed band alone. Techniques are never counted against assets in the suspicious band.
Turn Exposure Data Into Audit-Ready Evidence
| Framework | What ClearSkies ASM contributes |
|---|---|
| NIST CSF | Asset identification and continuous risk assessment under Identify, and continuous monitoring under Detect: a corroborated external inventory with attribution evidence, delta-based change history, and risk scoring that combines exploitation evidence with business context. |
| ISO/IEC 27001 | A maintained asset inventory with defined ownership, technical vulnerability management, and supplier relationship security, evidenced from the platform’s own records rather than assembled manually each audit cycle. |
| NIS2 | Risk-management measures and supply-chain security, with severity-tiered time-to-fix targets, automatic tracking and breach alerting, and a complete audit trail of who decided what and when. |
| DORA | ICT third-party risk management: named providers monitored continuously rather than by questionnaire, consolidated into one scored register with SLA attainment reporting. |
| EU Cyber Resilience Act | Vulnerability handling for products with digital elements: SBOM ingestion in SPDX and CycloneDX formats, with components matched continuously against CVE, EPSS and KEV data. |
The same technique tag, confidence band and decision record serve as evidence for the governance frameworks a program is assessed against. The platform produces what an auditor asks for; it does not make an organization compliant.
Turn Every Finding Into Measurable Action
Every severity band carries a time-to-fix target, tracking starts the moment a finding is raised, breach alerting fires while a target can still be met, and attainment is reported where executives and clients can see it. Targets are set per tenant for managed-service delivery.
See your own surface for fifteen days
Discovery and assessment run against your own root domains before any commitment.
Book a demo