ClearSkies Active Defense
Any interaction is an intrusion. There are no false alarms in a decoy.
Why Deception
Where prevention-first defense falls short after the breach
Prevention-based security, meaning firewalls, endpoint protection, patching and segmentation, remains essential and Active Defense replaces none of it. The point is what happens after those controls are bypassed, when traditional monitoring struggles to tell an intruder's reconnaissance apart from ordinary administrative activity.
The perimeter blind spot
Once an attacker is inside, controls tuned to stop entry no longer apply, and east-west reconnaissance and lateral movement proceed largely unwatched.
Signature and payload evasion
Repacked malware, fileless techniques and living-off-the-land abuse of trusted binaries leave nothing for a signature engine to match.
Credential-based intrusion
When an adversary uses valid stolen credentials, the activity looks legitimate to identity and access controls that only check whether the login succeeded.
Alert fatigue
Conventional internal-network monitoring produces ambiguous, probabilistic alerts in volume, so a genuine intrusion hides in the noise.
Deployment
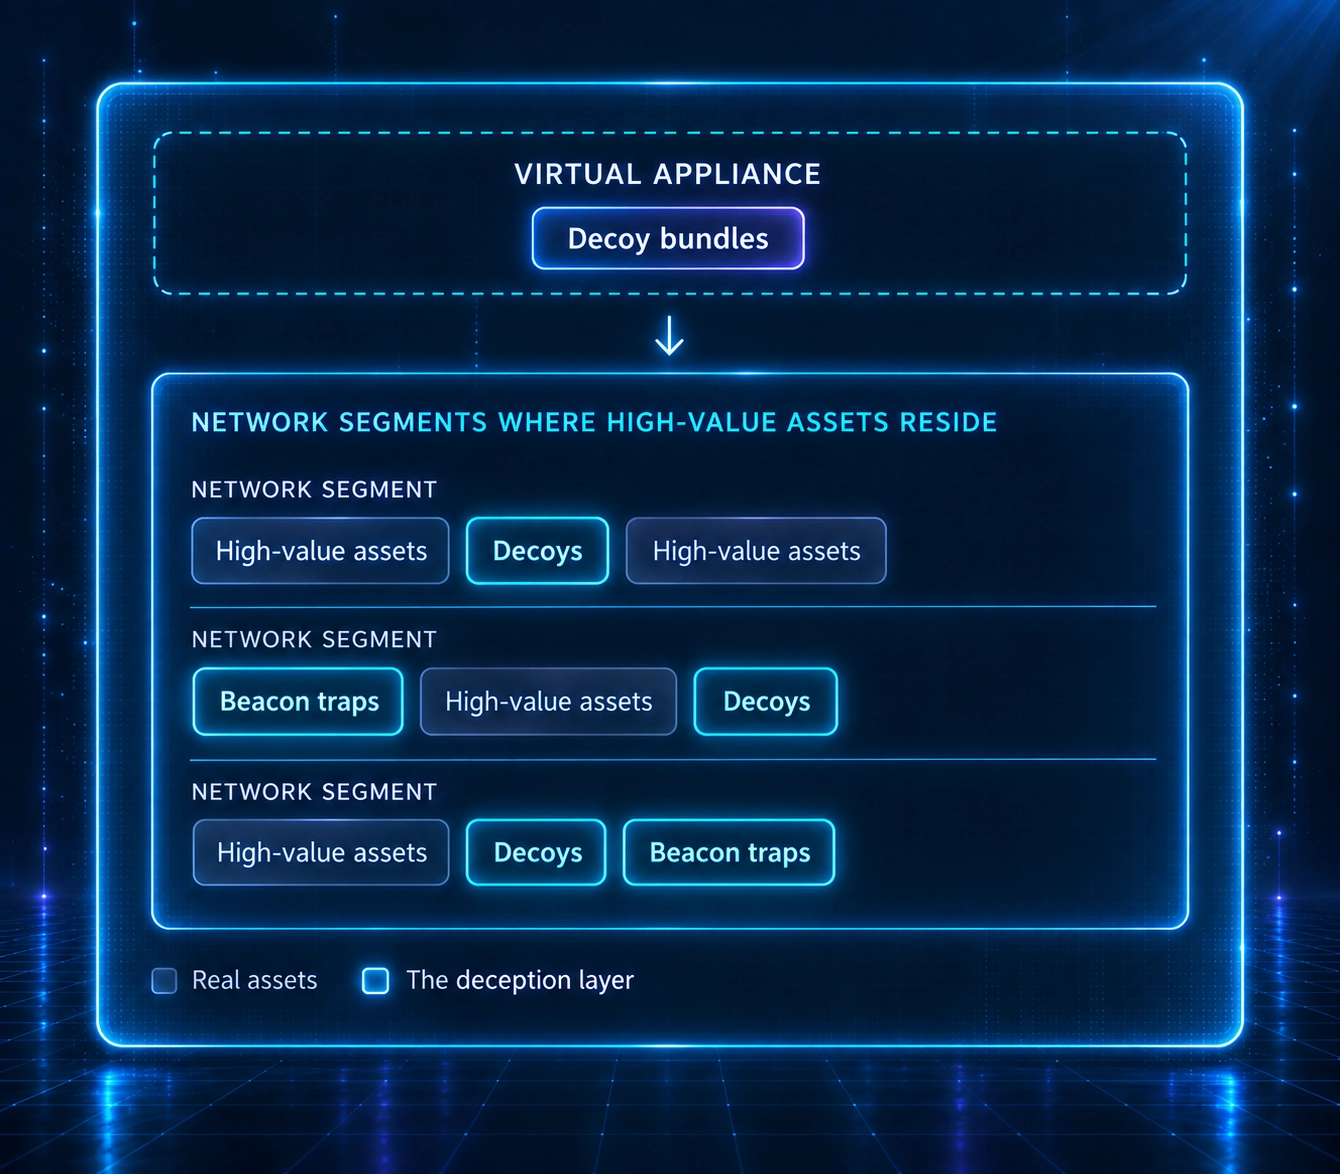
Active Defense is delivered as a virtual appliance, installed in a standard virtualization environment and placed across the network segments where high-value assets reside. Depending on the model, a single appliance emulates a range of simultaneous decoy bundles. It runs self-managed or as a managed service, deployed and monitored through the ClearSkies portal.
What sets Active Defense apart
Active Defense inverts the problem. Instead of separating malicious behavior from legitimate behavior on real assets, it plants assets that have no legitimate use at all. A decoy is indistinguishable from a real server or operational technology device. A beacon trap is a credential or a file that exists only to be stolen. Legitimate users never touch either, so the signal is binary: any interaction is an intrusion. Detection by certainty rather than probability, within a defense-in-depth architecture.
Detection by certainty
The signal is binary rather than probabilistic, because the asset touched had no legitimate use.
Evidence, not just an alert
Every interaction yields the source, the method, the purpose and the target, recorded for reconstruction and for a legal case.
Coverage that reaches operational technology
A Modbus high-interaction decoy presents a convincing industrial target without touching a real controller.
No production risk
The layer adds detection without adding anything an attacker can damage, because none of it is real.
At a glance
| Benefit | What produces it |
|---|---|
| Dwell time collapses | An intruder is surfaced during reconnaissance, not after exfiltration. |
| Analyst time goes to real threats | Essentially no false positives, so the queue gains certainty rather than volume. |
| Coverage where monitoring is weakest | The internal network after the perimeter, including operational technology and contractor devices. See what is covered |
| One incident rather than one more alert | Every trap event is correlated with exposure, identity, resolution-layer and endpoint signal. |
Commercial & licensing
Licensing built around your deployment
Active Defense is licensed by the protected environment and the deployed decoy bundles.
- Protected environment
- Deployed decoy bundles
Tier structure and the managed-service commercial model are described in the ClearSkies iISOC platform and MSSP briefs.
Discuss your deploymentQuestions Raised in Evaluation
Does deception replace the prevention and monitoring controls already in place?
Is there any risk to production systems or data?
Does Active Defense act on what the other add-ons find?
Connect with the team
Book a demo
Have a question first
Talk to the team