ClearSkies Identity Threat Protection
Identity Threat Protection and Response, a native add-on.
Identity-first
Detection anchored to the account
Seven pillars
The full scope of an identity defense program
Real time
Detection, verification and containment
Why Identity Needs Its Own Detection Surface
An organization that cannot tell a legitimate login from a stolen one has no meaningful control over its data, whatever else the security stack detects.
- Phishing kits and information-stealer malware harvest credentials and session tokens at scale
- Adversaries authenticate as legitimate users and move laterally using valid sessions
- Insiders abuse access they already hold
Where the incumbent stack falls short
What the discipline does, and what ITP does not replace
Identity threat protection and response operates continuously across the identity fabric rather than at the moment of provisioning.
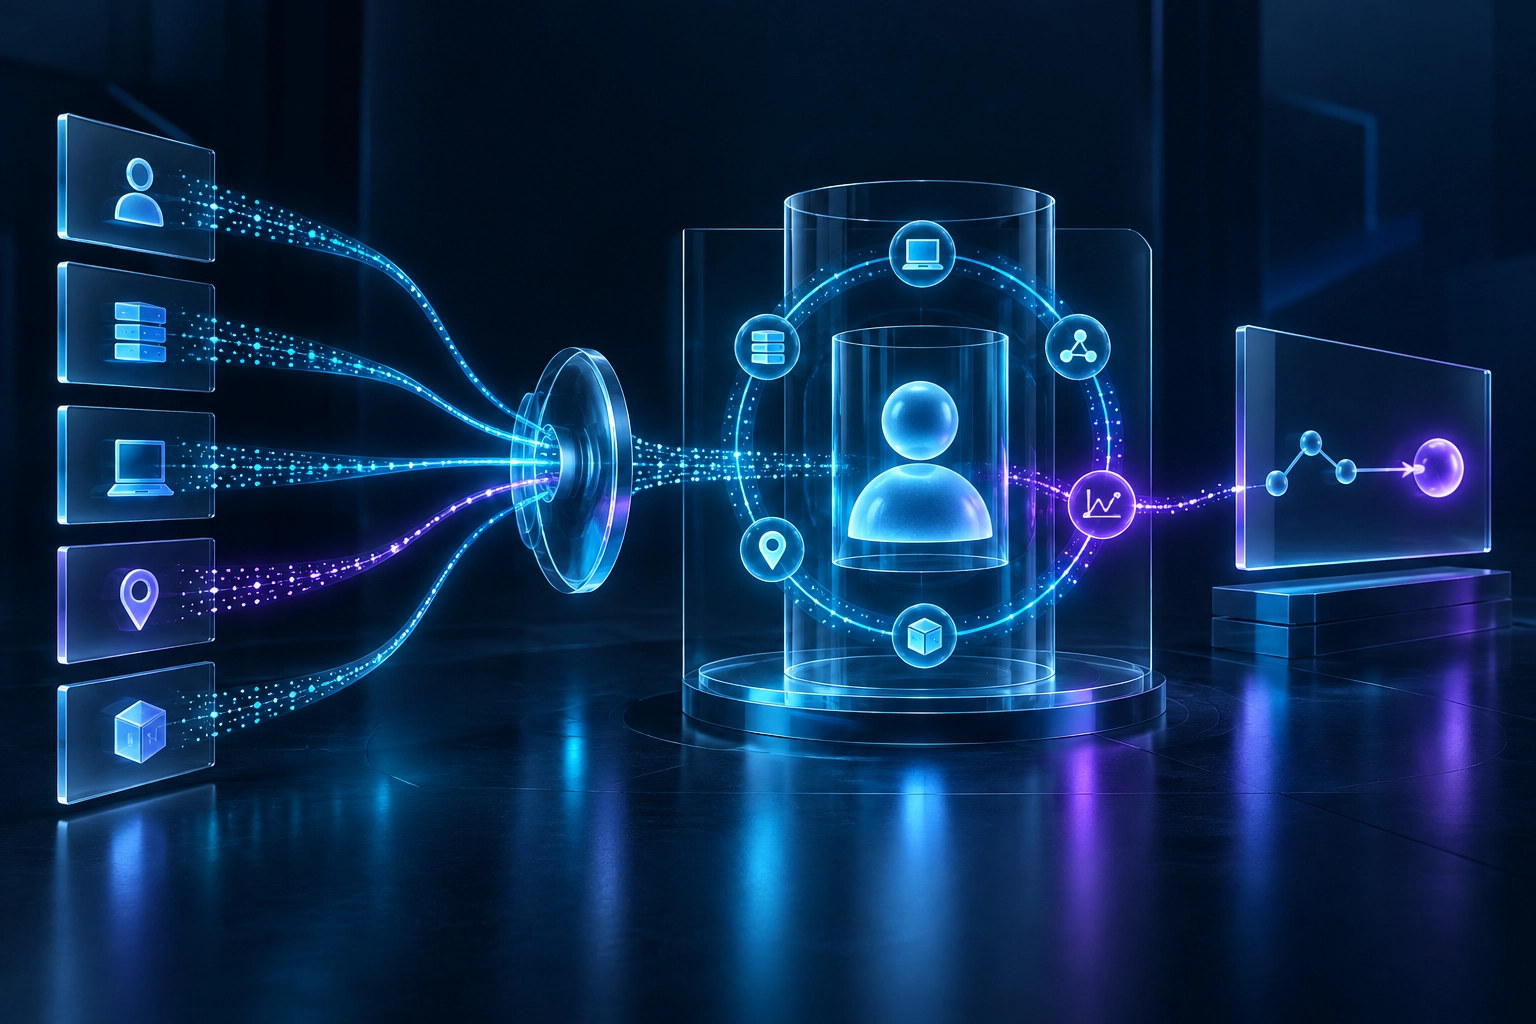
What ITP does
- Baselines behavior per identity
- Detects deviation and known identity attack techniques as they occur
- Attributes every signal to a specific user or service account, with its roles and current risk
- Delivers the result into the workflow where analysts already work
What it does not do
- Replace identity and privileged access management. Those govern how access is granted; ITP evaluates what an account does once it holds it.
- Block an authentication in the protocol itself. ITP detects and responds, but does not sit inline in the authentication path — a scope boundary rather than a gap.
Why ClearSkies Identity Threat Protection
Identity protection is where a security investment becomes demonstrable, because the outcomes it produces are countable.
The interval during which an attacker holds valid access is cut
Detection at the authentication event rather than at a downstream artifact.
Containment does not require taking systems offline
Response is targeted at the identity, by disable, revocation, reset or step-up authentication.
Analyst time goes to judgment rather than reconstruction
Pre-investigation records a reasoned verdict before a human opens the finding.
Fewer false positives, and therefore permission to act
Weighted multi-signal scoring, in which no single signal is decisive and none alone can trigger a response.
Coverage is measurable, and audit evidence is a by-product of operation
Every detection carries its ATT&CK technique, and framework mapping is applied as evidence is produced.
Three things separate the capability from an alerting layer attached to a directory
- 01
Six independent signal classes are combined before any verdict is issued
- 02
Identity risk is sharpened by every other platform layer, with the outcomes coming back and no integration built by the customer
- 03
The primary artifacts are identity timelines, verdicts and one-click response rather than provisioning workflows
For the organization and for the provider
For the organization, identity moves from a governance concern reviewed periodically to a monitored control surface, and whether an account was compromised is answered in minutes rather than after an engagement.
For the service provider, multi-tenancy is a first-class concern from the data layer upward, so a provider configures a new customer rather than building one.
Go to the MSSP platform
Questions Raised in Evaluation
The organization already owns an identity provider with built-in threat detection.
That capability is retained and consumed. The question to test is what it sees outside its own boundary: whether an account that authenticates through it one day and directly against Active Directory the next is one subject with one baseline or two partial records.
The SIEM already receives directory logs.
Receiving the events and evaluating them are different capabilities. Event data without a per-identity baseline, privilege context and entitlement state does not produce an identity verdict.
Automated account disable is too risky for the business.
Automation is permitted only at the Critical band, only where multiple independent signals concur, and only where tenant policy allows it.
Attackers no longer break in. They log in.
A platform without identity context observes that something happened on a host. A platform with it knows which account acted, what that account can reach, whether the behavior fits its history, and which single action removes the access.
Request a Demo